An AI policy for employees is a one-page set of rules that tells staff which AI tools they can use, what data stays out, and who to ask. Seven rules cover most small businesses: allowed tools only, business accounts only, no client, health or payment data, one named contact, check outputs, report mistakes, review quarterly.
Key takeaways
- One page your team will read beats twenty pages nobody opens.
- Thryv’s 2026 small business survey found 70% of owners say they need more training to use AI effectively.
- The biggest risk is data: client, health and payment details pasted into the wrong tool.
- Name one person to ask, so “I wasn’t sure” has an answer.
- Review the list every quarter, because AI tools change fast.
What should an AI policy for employees include?
An AI policy for employees should include which tools are allowed, which accounts to use, what data never goes in, who to ask, how to check results, how to report mistakes and when the policy gets reviewed. Keep it to one page in plain language, so a new hire can read it in five minutes.
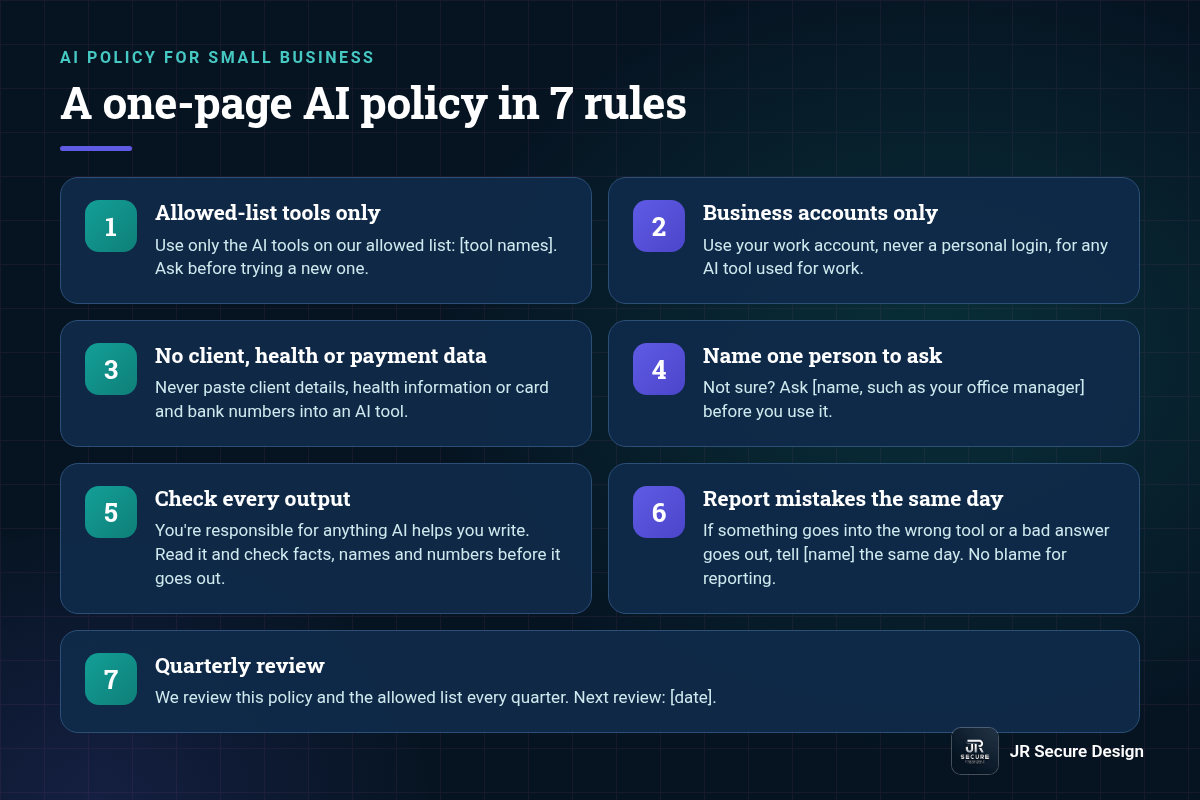
Here’s the one-page template. Copy it, fill in the brackets and share it with your team.
[Company] AI policy for employees (one page)
- Allowed-list tools only. Use only the AI tools on our allowed list: [tool names]. Ask before trying a new one.
- Business accounts only. Use your work account, never a personal login, for any AI tool used for work.
- No client, health or payment data. Never paste client details, health information or card and bank numbers into an AI tool.
- Name one person to ask. Not sure? Ask [name, such as your office manager] before you use it.
- Check every output. You’re responsible for anything AI helps you write. Read it and check facts, names and numbers before it goes out.
- Report mistakes the same day. If something goes into the wrong tool or a bad answer goes out, tell [name] the same day. No blame for reporting.
- Quarterly review. We review this policy and the allowed list every quarter. Next review: [date].
Why should an AI policy fit on one page?
Because people follow rules they can remember. A long policy gets signed and forgotten. One page with seven short rules can be pinned near a desk, read in a team meeting and checked in seconds before someone pastes something into a chat. Keep the full detail in a longer acceptable use policy for managers.
For that longer version, use our AI acceptable use policy template. It covers tool reviews, data classes and sign-off in more detail. The one-page version here is what staff see day to day.
Do small businesses need an AI policy?
Yes, if anyone on the team uses AI for work, and most do. Thryv’s 2026 survey reports AI adoption among U.S. small businesses at 66%, with 70% of owners saying they need more training. A one-page policy is the cheapest training you can give: clear rules on tools, data and who to ask.
Without a policy, staff make their own rules. One person pastes a client email into a free chatbot on a personal account, another uses an AI note-taker nobody reviewed. Our guide to shadow AI discovery shows how to find the tools already in use before you write the allowed list. Our guide to whether ChatGPT is safe for business explains how Free and Plus handle training compared with ChatGPT Business and Enterprise, and what staff should never paste in.
QUICK CHECK: Ask your team one question this week: “Which AI tools did you use for work this month?” Write down every answer. That’s the first draft of your allowed list.
How often should an AI policy be updated?
Review your AI policy every quarter, and any time you add a new AI tool, a tool changes how it handles data, or a mistake happens. Quarterly keeps the allowed list current without becoming a chore. Put the next review date on the policy itself, so everyone knows when it’s due.
The 30-minute quarterly review
- Re-ask the tool question. What did people use this quarter?
- Update the allowed list. Add tools you’ve checked, remove ones nobody uses.
- Read the mistake log. Did any rule cause confusion? Reword it.
- Re-share the page. Send the updated version and set the next review date.
A quarterly rhythm also fits common frameworks. JR Secure Design builds AI programs aligned to the NIST AI Risk Management Framework, which treats AI governance as ongoing, not a one-time document. Nonprofits can use our AI policy for nonprofits guide for a version tuned to donor and volunteer data.
NEXT STEP: Want help putting your policy into practice? See our AI governance assessment, or book a 30-minute call.
AI policy for employees: frequently asked questions
Can employees use ChatGPT at work?
They can if it’s on your allowed list and they follow the data rule. Use a business plan where you can, since consumer plans may handle chats differently. Whatever tool you allow, the same rules apply: work account only, no client, health or payment data, and a person checks every output before it goes out.
Who should own the AI policy in a small business?
One named person, usually the owner, office manager or whoever handles IT. They keep the allowed list, answer questions, log mistakes and run the quarterly review. They don’t need to be technical. They need to be easy to reach, so employees ask first instead of guessing.
What happens if an employee breaks the AI policy?
Start with the fix, not blame. Find out what data went where, contain it and update the rule if it was unclear. Same-day reporting only works if people aren’t afraid to report. Repeated or deliberate misuse is a normal HR matter, handled like any other policy, and your policy should say so.
Should employees disclose when they use AI?
For anything that goes to a client or the public, a simple rule helps: the person who sends it owns it, and they’ve checked it. Some businesses also ask staff to note AI help on client deliverables. Decide what fits your clients and industry, then add one line to the policy so it’s consistent.
Is an AI policy the same as an AI acceptable use policy?
Close, but not quite. An acceptable use policy is usually the full document, with definitions, review steps and sign-off. The employee AI policy is the one-page version staff actually read. Many small businesses keep both: the full policy for managers and records, and the one-page rules for daily use.
Want help writing your allowed list?
Ask Sophia, our free AI advisor, at jrsecuredesign.com/sophia, or talk it through with James.
JR Secure Design builds AI and security programs aligned to NIST AI RMF and ISO/IEC 42001. More at jrsecuredesign.com.